Authorization & Scope
Targets, boundaries, timing, credentials, data handling, and escalation paths are defined before testing.
 MOHAMED RADISECURE DIGITAL ENGINEERING
A disciplined workflow for understanding exposure, validating risk, documenting impact, and helping teams fix what matters.
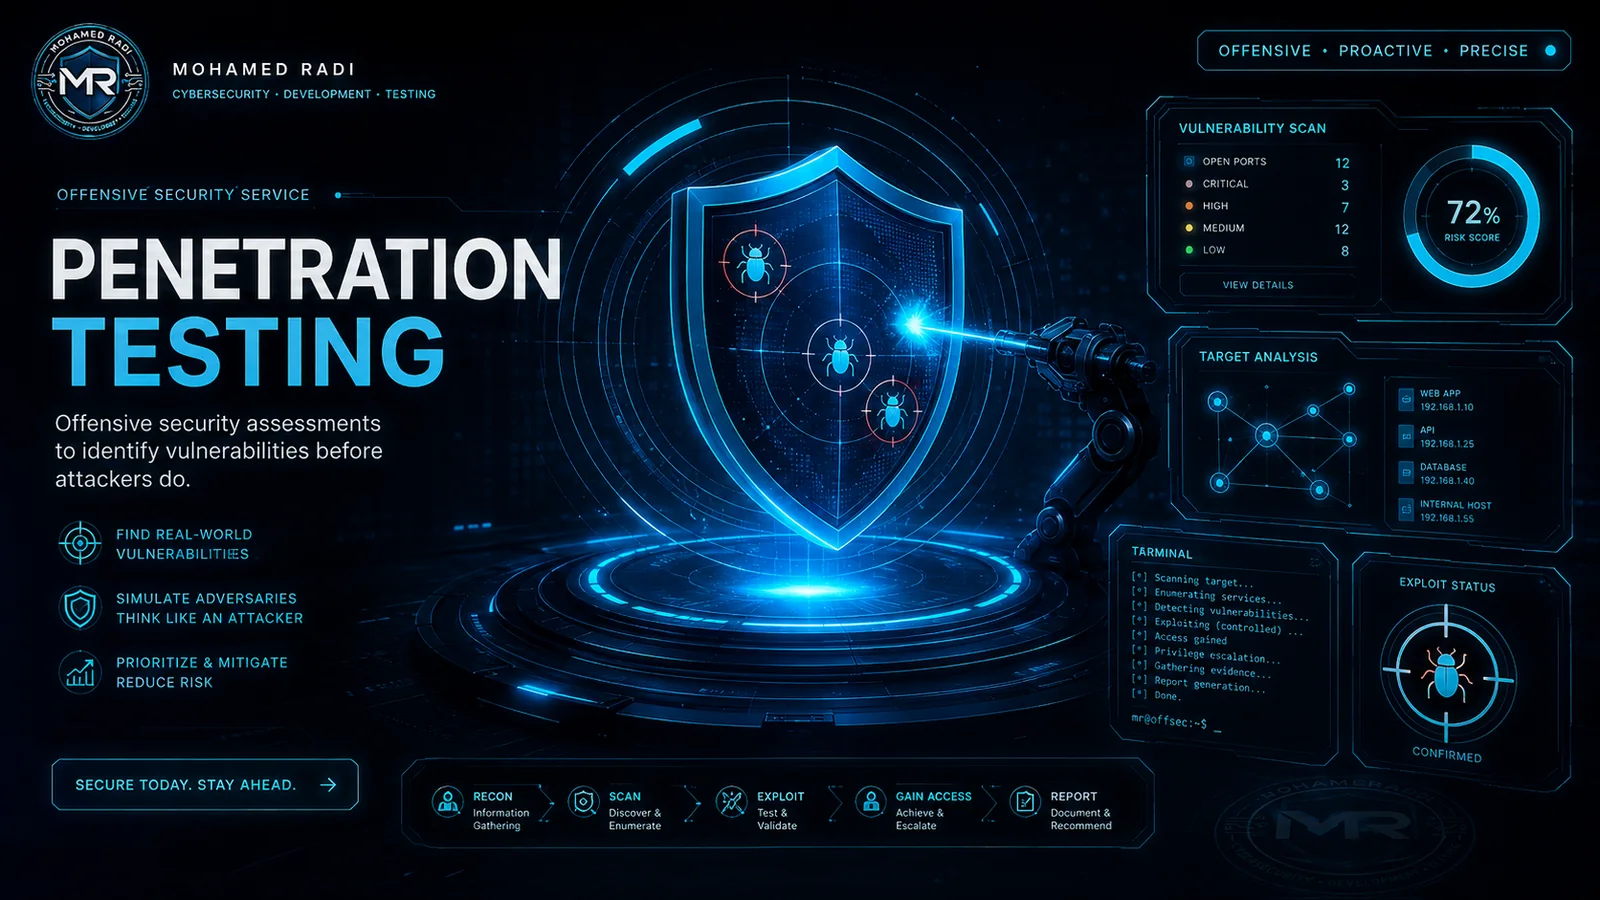
These visuals support the service narrative without exposing target, client, or assessment-sensitive information.
Testing is performed only with clear authorization and an agreed scope.
Targets, boundaries, timing, credentials, data handling, and escalation paths are defined before testing.
Public exposure, application behavior, access controls, input paths, configurations, and security posture are mapped.
Potential findings are carefully validated to reduce noise and avoid overstating impact.
Evidence, severity, affected components, business impact, reproduction guidance, and remediation priorities are documented.